



Cloudbrowser
Persistent cloud Chrome for AI agents, with saved logins, forks and live view

Open-source AI pentesting agents that prove each bug with a working exploit
About
Point Strix at a local folder, a GitHub repo, a live URL or an OpenAPI spec and it spins up a sandbox with a browser, an HTTP proxy, a terminal and a Python runtime. Several agents split the work: recon, exploitation and validation, so you get confirmed issues (IDOR, injection, auth bypass, SSRF and more) instead of a long list of scanner guesses. Each run saves its report under strix_runs/. You bring your own model key (OpenRouter, Anthropic, OpenAI and others) or sign in to Strix Cloud and skip Docker. It also runs in GitHub Actions to scan pull requests, can call your own MCP servers during a run, and ships nine agent skills (npx skills add usestrix/strix) so Claude Code, Cursor or Codex can start pentests and fix findings. Only test systems you own or have permission to test.
Features
Install
How Grok Bot, a persistent personal agent, differs from coding agents like Claude Code and Codex, and when it makes sense to use each one or both together.
Six building blocks that turn a chat model into an agent that can work on its own: an inbox, memory, a safe place to run code, app access, background jobs and tracing.
Seven tools that cut Claude Code, Codex and Cursor token usage by compressing shell output, searching code and fetching current docs, with honest caveats.
Persistent cloud Chrome for AI agents, with saved logins, forks and live view
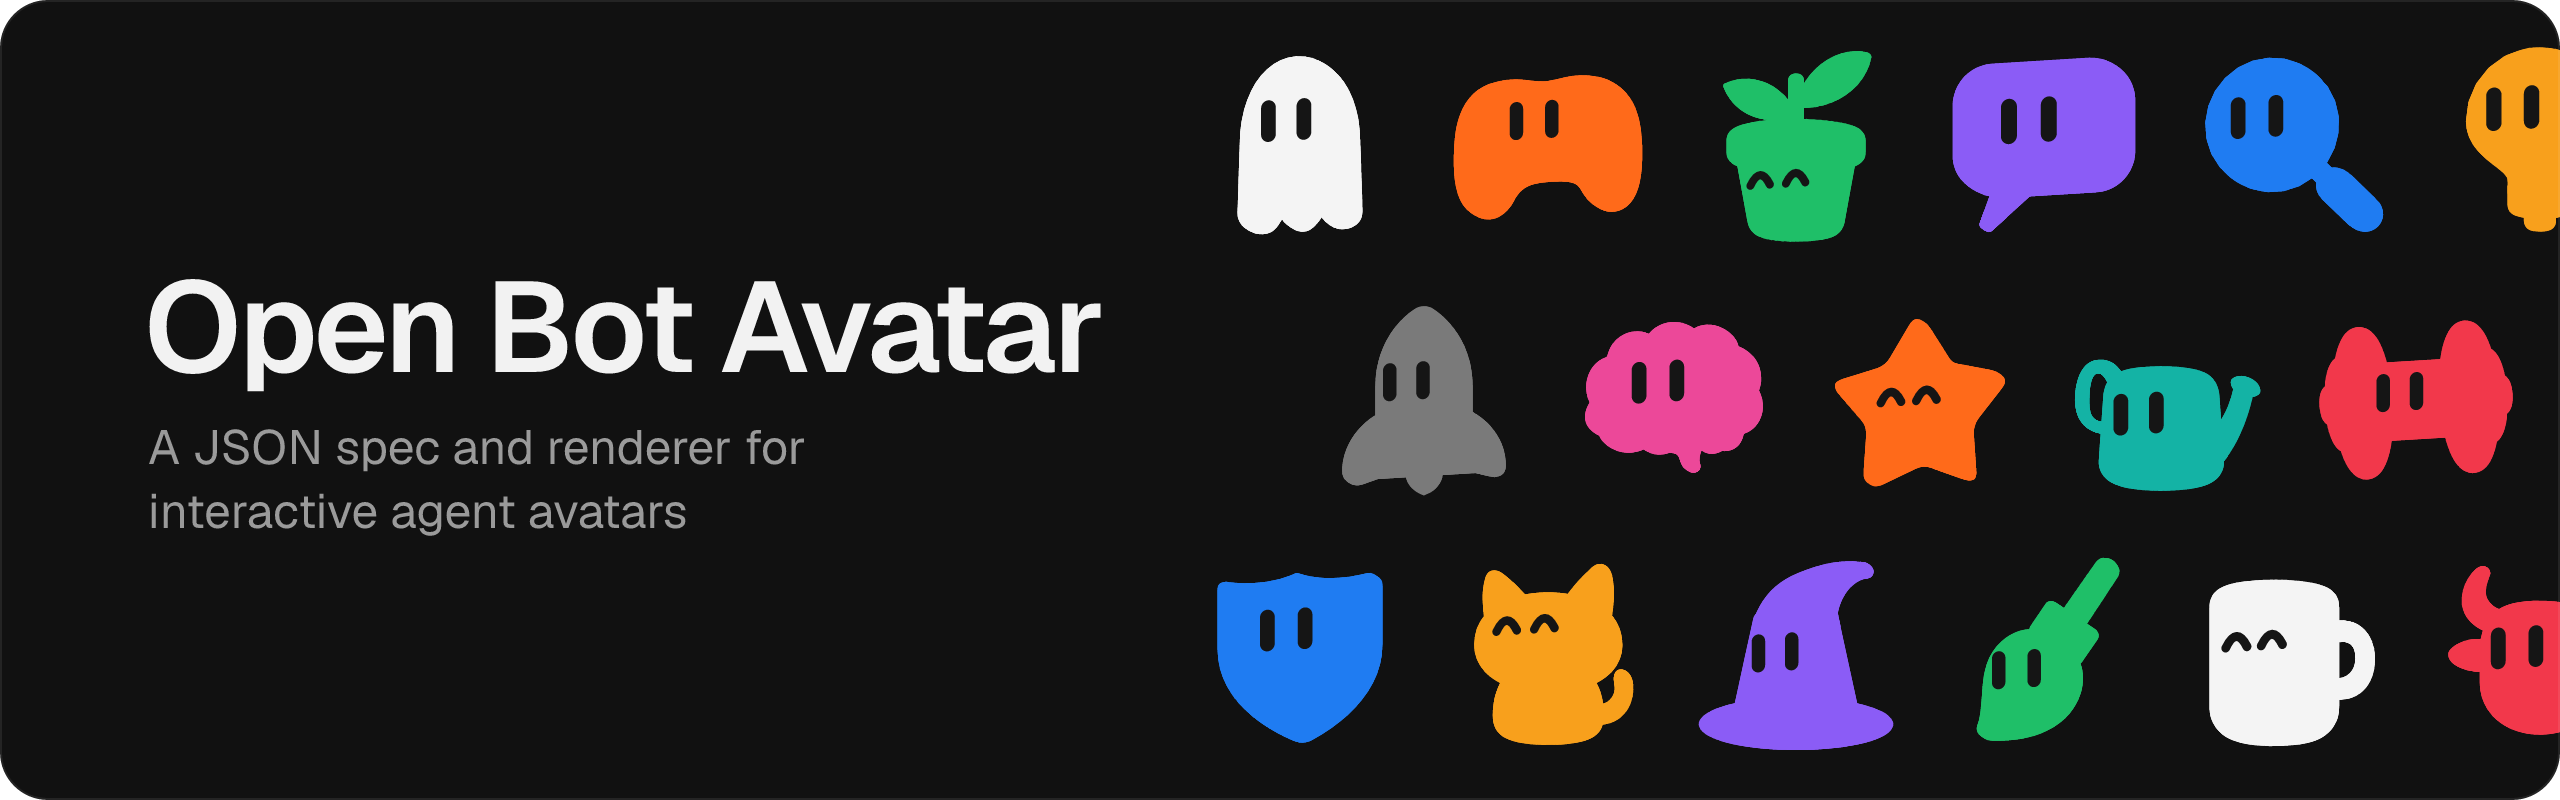
A tiny JSON spec and renderer for animated, interactive agent avatars
Open source multiplayer design canvas where humans and AI agents design together over MCP
Free. I review every submission.
is in the review queue. I'll install it, test it and list it if it passes.